
Free & open-source WordPress plugin
Bottle (Bot + Throttle): bot throttling for WordPress.
A set of tools that cuts server load when bots, LLM crawlers and exploit scans flood your site, without getting in the way of real visitors.
WordPress
PHP
Redis
JWT sessions
Cloudflare Turnstile
Why we built it
Bots were driving up hosting costs and causing outages
In our work building websites for clients, from ecommerce systems to CRM integrations to venue ticketing, we found that WordPress sites were routinely hit by bots. Plugins usually kept them at bay. Then AI arrived, and LLM builders hungry for content began crawling sites aggressively and ignoring robots.txt. Every site, not just ours, has seen massive increases in traffic, which means higher hosting costs, or worse, outages.
So we created Bottle, a free and open-source plugin that any WordPress site can use to throttle the bots that visit it. Have questions? See the Bottle FAQs.
How it works
Seven checks on every request
Bottle checks each request made to WordPress and throttles a session or IP address when it crosses a threshold.

Too many sessions per IP
Some bots ignore cookies, so Bottle sets a JWT session cookie on each request. An IP that opens too many new sessions in a short time is likely a bot.

Too many requests per session
Bottle measures a request rate for each session and throttles sessions that go over it.

Too many requests per IP
A per-IP request rate catches abusive addresses that never accept cookies, and so never have a session.

Too many requests per bot
A rate per reported user agent. Because bad bots forge user agents, this works best alongside the other checks.

Bot verification
Bots such as Google, Bing and Meta are checked against their published IP lists where possible. Verified bots get a higher rate limit, since they tend to behave better.

Overall request rate
Throttles specific sections of a site that are under attack, such as a course catalog. Useful against bot networks with rotating IPs.

Excessive 404s
Scans and misconfigured bots generate costly 404s. Bottle can throttle all 404s, or only those for static files such as images.
Throttle responses
Gentle on people, firm on bots
When a request is throttled, Bottle can reply with a plain 429 response, or serve a JavaScript cryptographic puzzle or a Cloudflare Turnstile widget. A legitimate browser solves the puzzle and sends the answer back for verification, with no input from the visitor. Once it has proven it's human, the visitor goes straight on to the site. Some bots solve these puzzles too, but many don't.
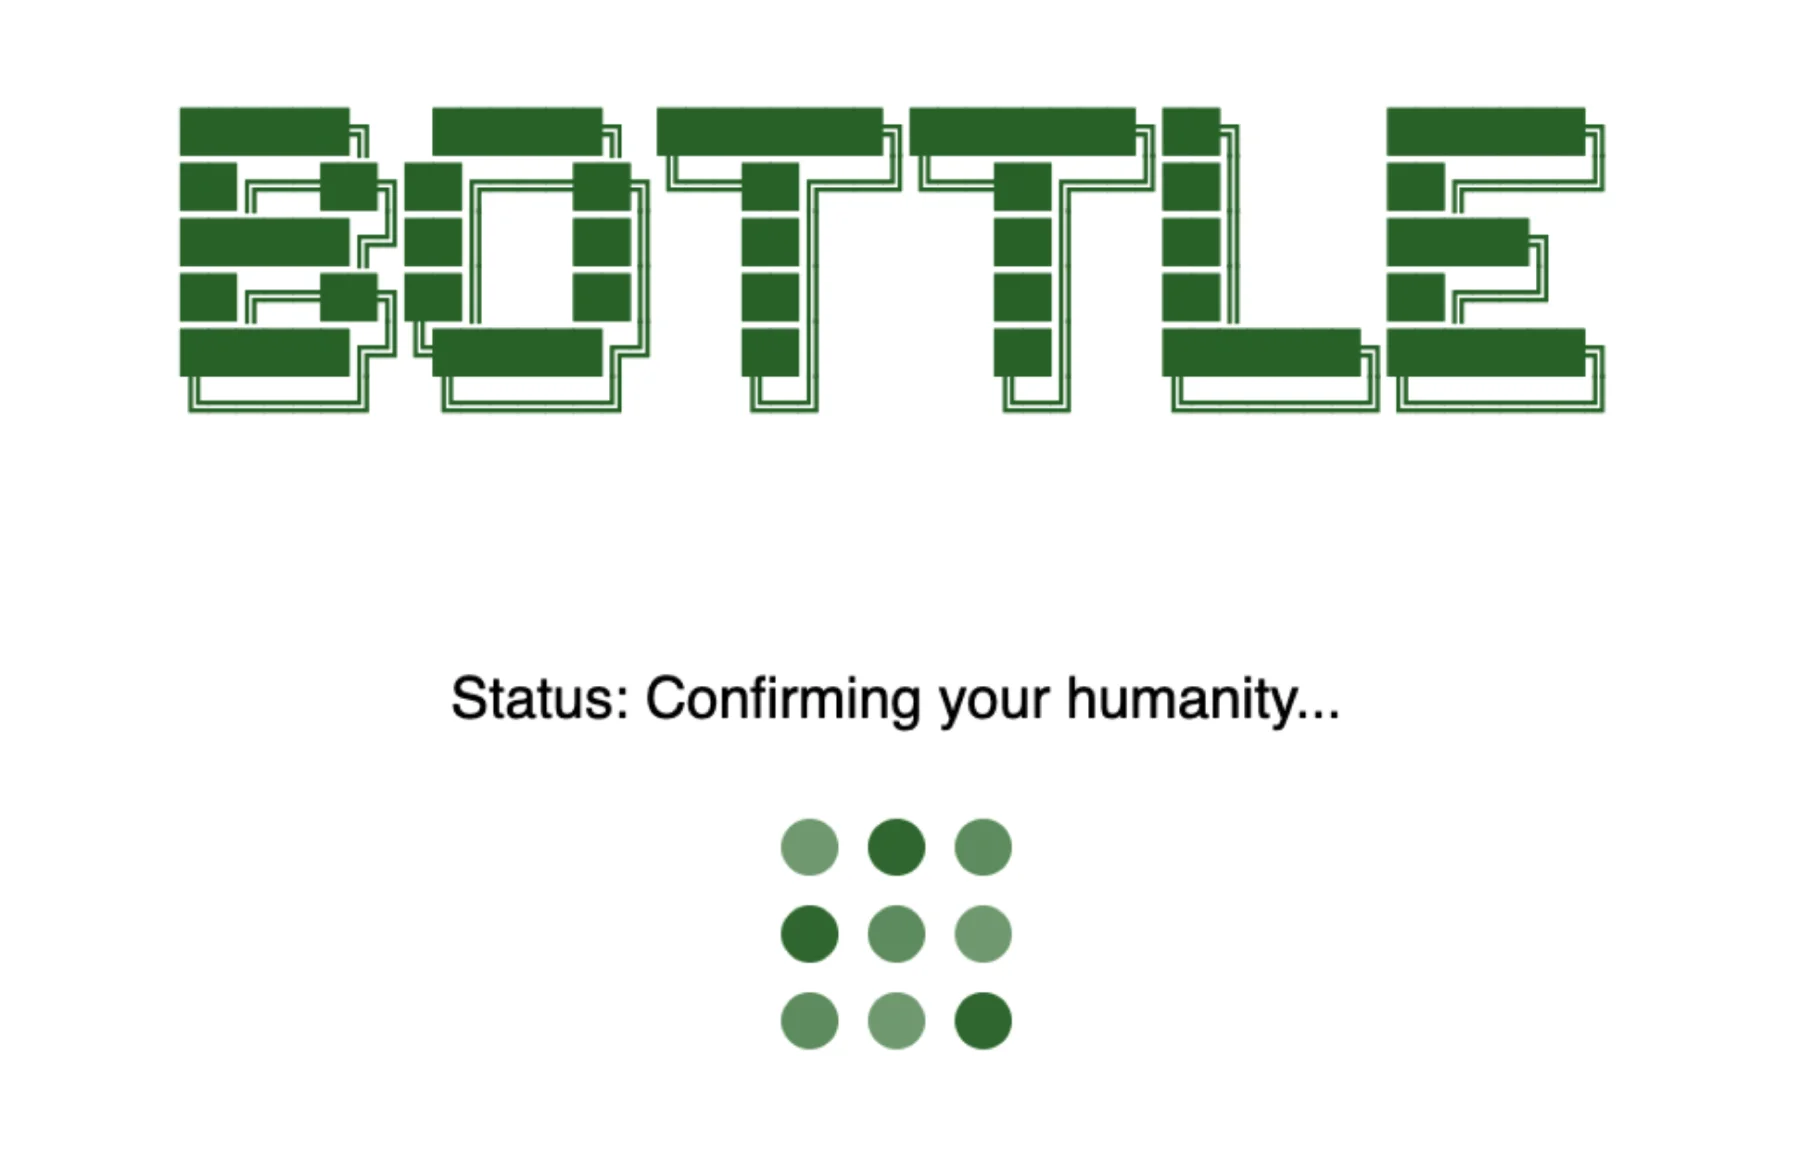
The proof-of-work check a throttled visitor sees for a moment
When a throttle is triggered, Bottle stops WordPress from processing the request, which greatly reduces server load during an attack. Each throttle ends automatically when its measurement window closes.
Why stopping early works
WordPress does a lot of work for every request
The web server sends every request to WordPress, legitimate or not, unless it's a static file such as an image. That means WordPress loads end to end for every request. Here's a rough version of the actions that run when WordPress loads, even for a page that doesn't exist:
Load taxonomies (categories and tags)
Register post types
Load all plugins
Set up the theme
Load translations
Set the current user, if logged in
Parse the request and query string
Get posts
Load the template
Output stylesheets and scripts
Output posts
Shut down
Big sites tend to run lots of plugins, and starting them all up for every request is expensive. Bottle checks each request before this work begins and stops WordPress from starting up when a request should be throttled. (The 404 check runs a little later, at template_redirect, just before the theme is set up.)
Bottle isn't a firewall. It won't block or clean up malicious attacks. But because those attacks usually come in large numbers, Bottle can slow them down and reduce server load, keeping the site up for real users.
Proven under load
Keeps sites up through sustained attacks
Bottle is designed to keep websites stable under extremely high load, with minimal impact on real users. These charts show a sustained attack of more than 100 bot requests per second being throttled.
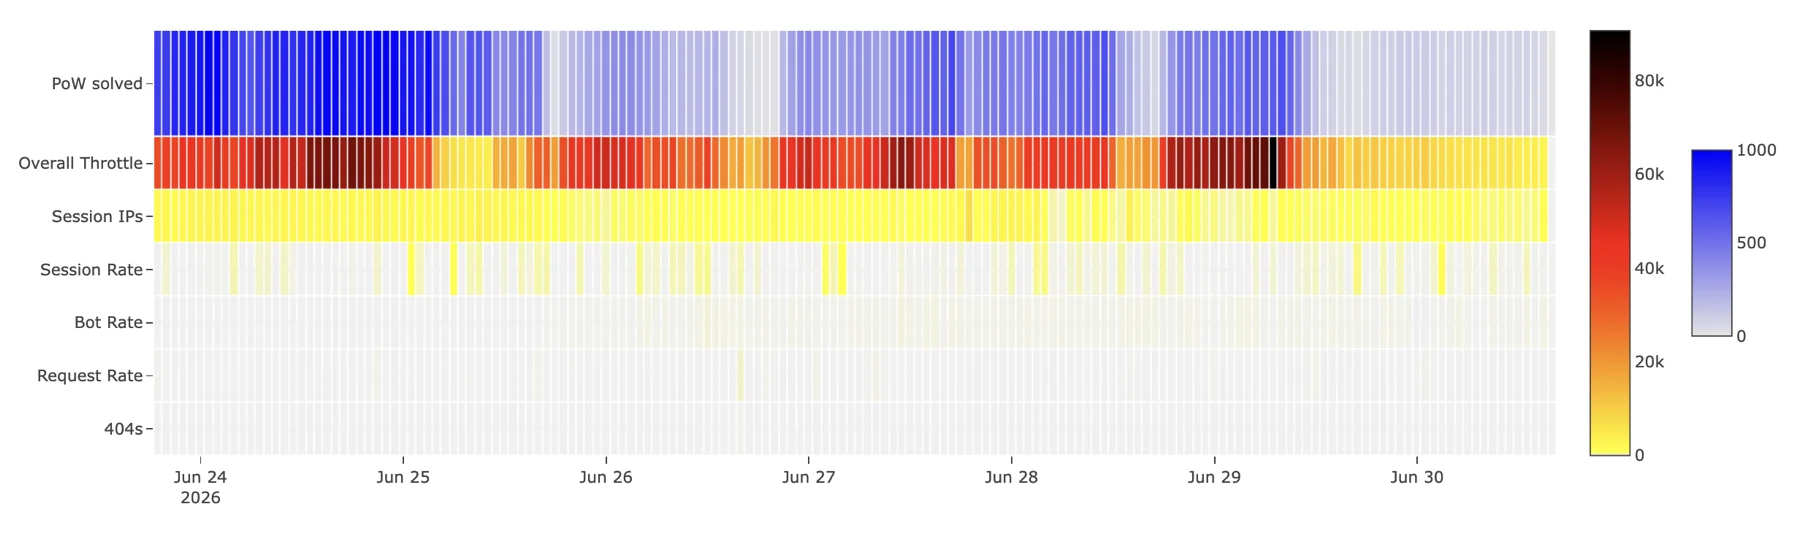
A week of throttling during a sustained bot attack
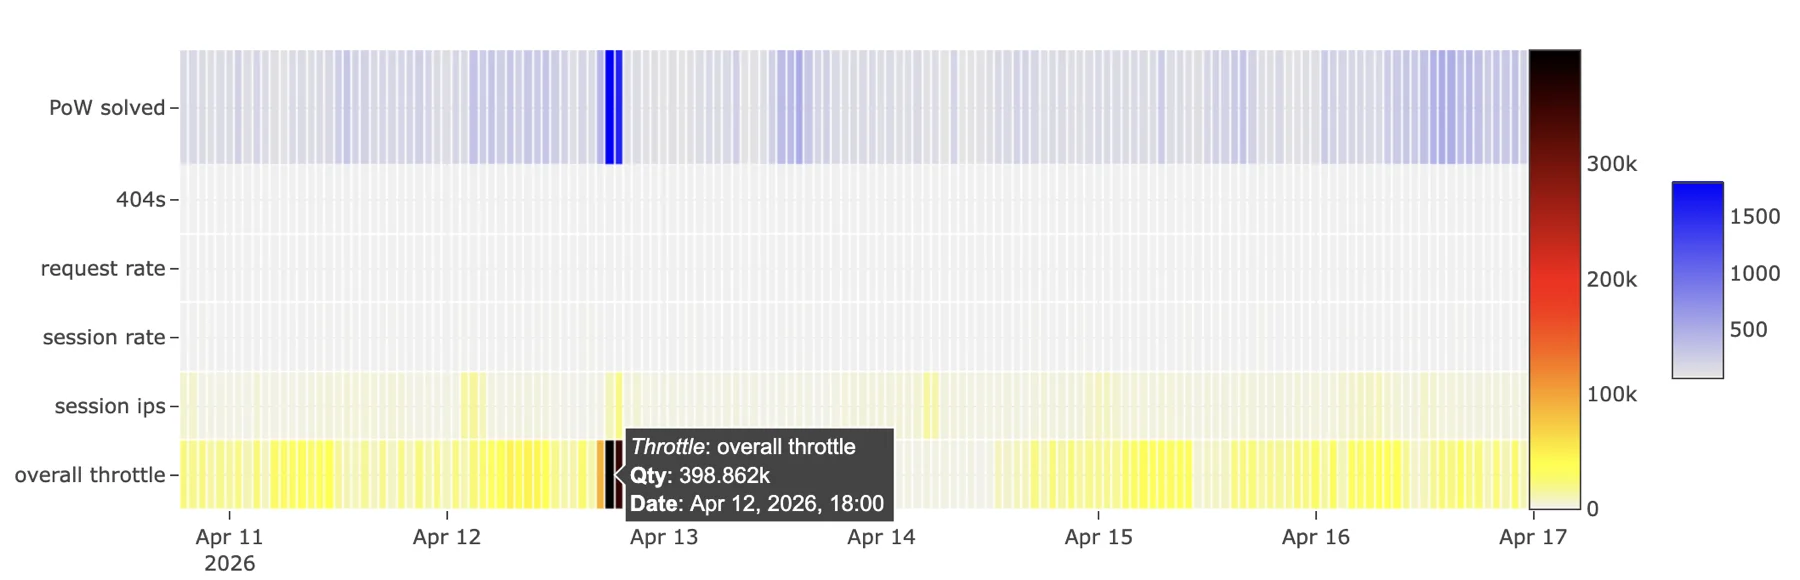
A single-hour spike of nearly 400,000 throttled requests
See what's happening
Real-time request tracking and a bot heatmap
Bottle's real-time Requests tool shows how each rule handles every request, which makes it easy to tune the throttling settings.
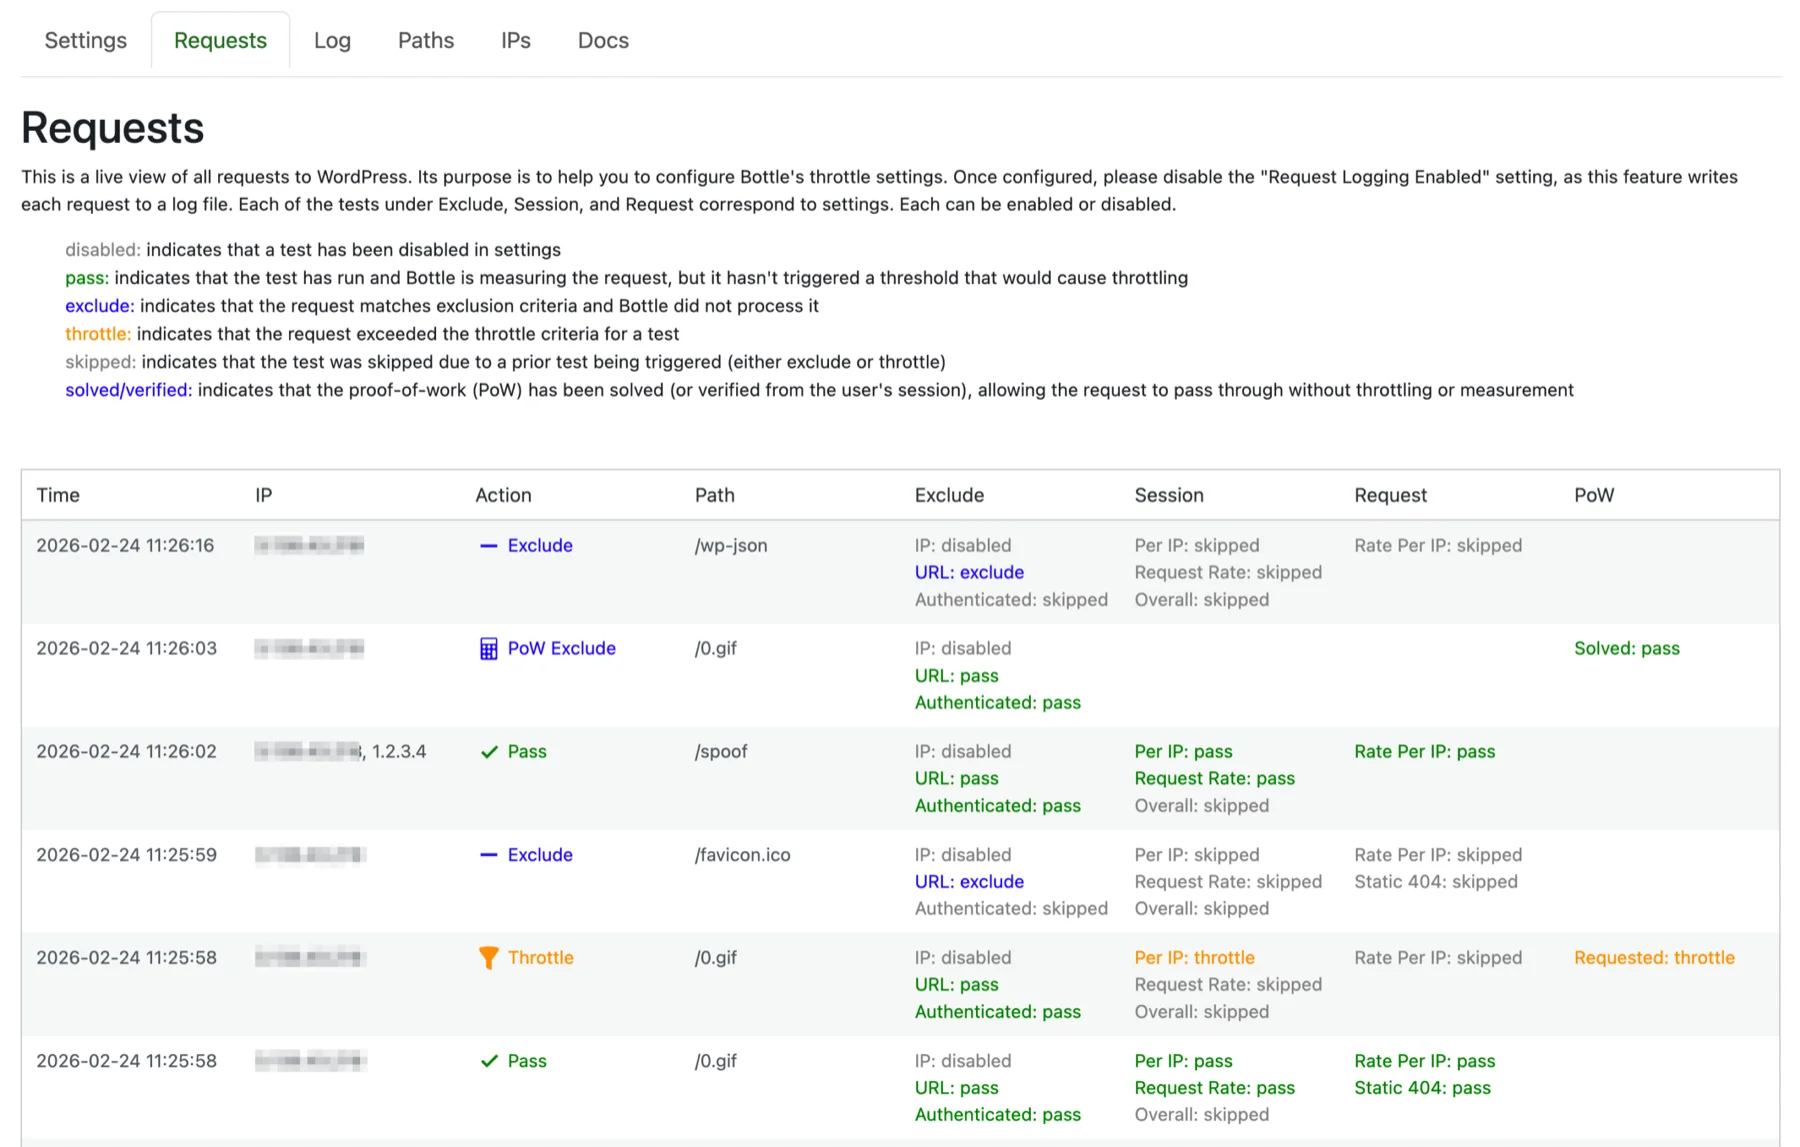
The Requests tool shows how each rule handled each request
Bottle also tracks the bots visiting your site and draws a heatmap of activity by reported user agent. User agents are easy to fake, so Bottle verifies the IP addresses of some bot types. Bottle never relies on the user agent to throttle, because even well-run bots can be misconfigured.
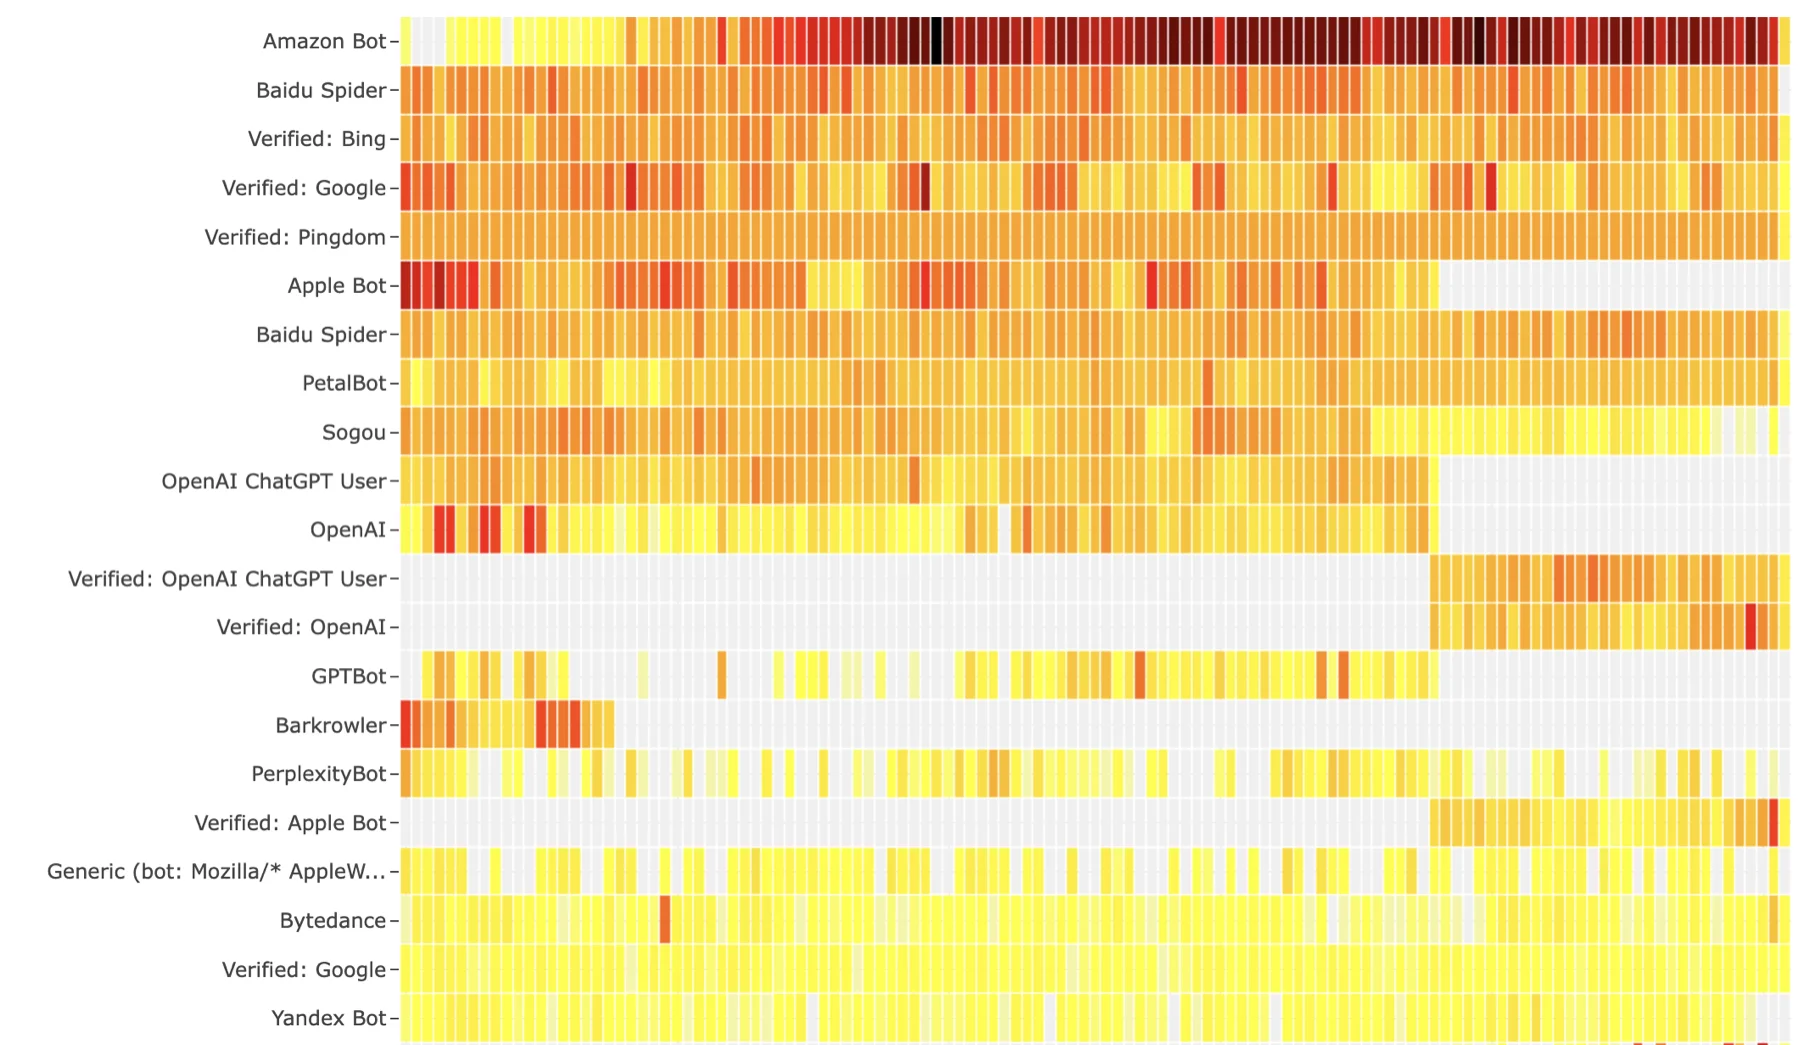
Bot activity heatmap by reported user agent
Need help with bot traffic or WordPress performance?
Our developers host, tune and protect complex WordPress sites. Tell us what you're seeing.